- Using Bitbucket Cloud pipeline
- PLSQL
- Exploring the SonarQube Cloud Free Trial
Have this example statement we use to connect to an LDAP that I’m using to test the secret scanning:
  l_bind := dbms_ldap.simple_bind_s(
      ld     => l_session,
      dn     => 'jnewman',--username
      passwd => 'z9b5M3bX3MERSTP'--dummy password
   );
The scan via the pipeline seems to be working, but is not detecting any secrets:

The file being scanned is a .sql file, and I’ve included it in the list of file patterns:
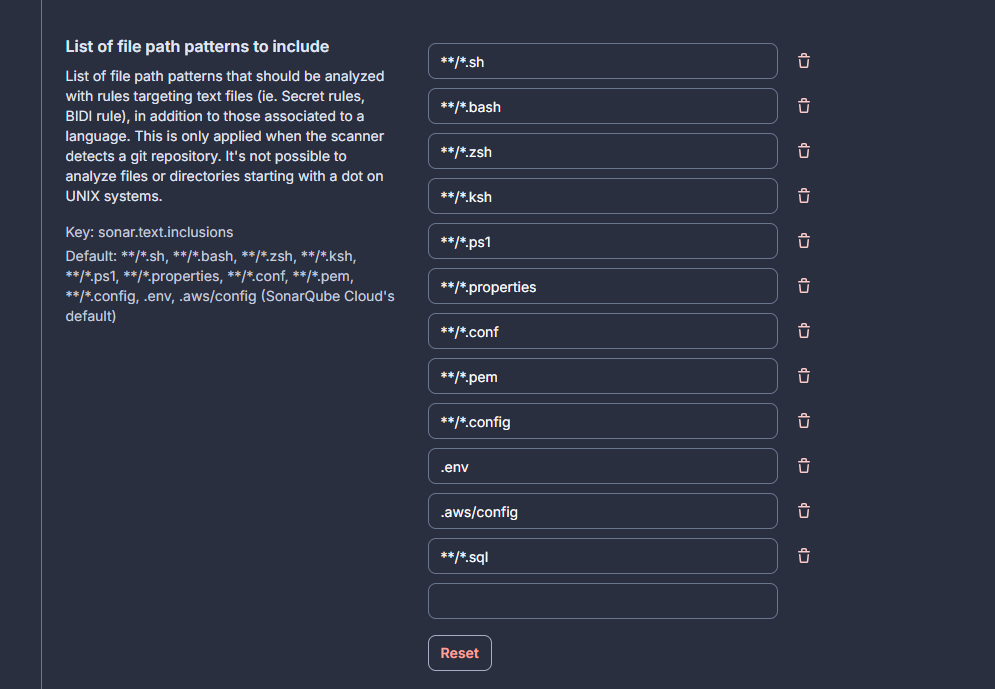
Anything that I’m missing that would prevent the secret from being picked up by the scanner?